 mozgi
Vulnerability in Grok exposed data from 35,000 applications
November 11, 2026
Security company Claroc discovered over 35,000 applications created using Grok tools that were accessible to unauthorized users. The leak was caused by default settings, where the access parameter was automatically set to "anyone with the link."
Confidential patient medical data, plaintext passwords, and internal documents from the SpaceXSI sales department were exposed. After the vulnerability was discovered, SpaceXSI promptly restricted access to its own 24 applications used by employees.
The remaining tens of thousands of vulnerable third-party programs remain accessible on the internet. The incident highlights the security risks that arise when AI tools automatically generate software with weak default privacy settings.
Related news
 American brokers are selling AI training data to Chinese labs
November 11, 2026
 New York to launch state program for testing AI systems
November 11, 2026
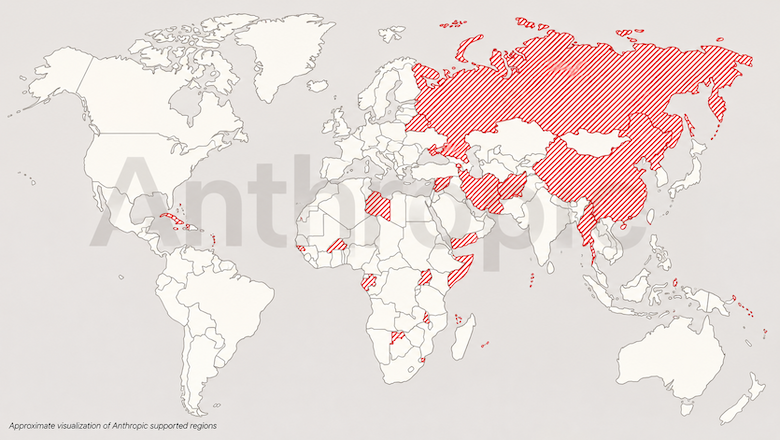 Anthropic has tightened access rules to Claude for unsupported regions
November 11, 2026
 AI companies have started blocking reverse-engineering tools
November 11, 2026