 mozgi
Critical vulnerabilities and hardcoded keys have been discovered in Flock cameras
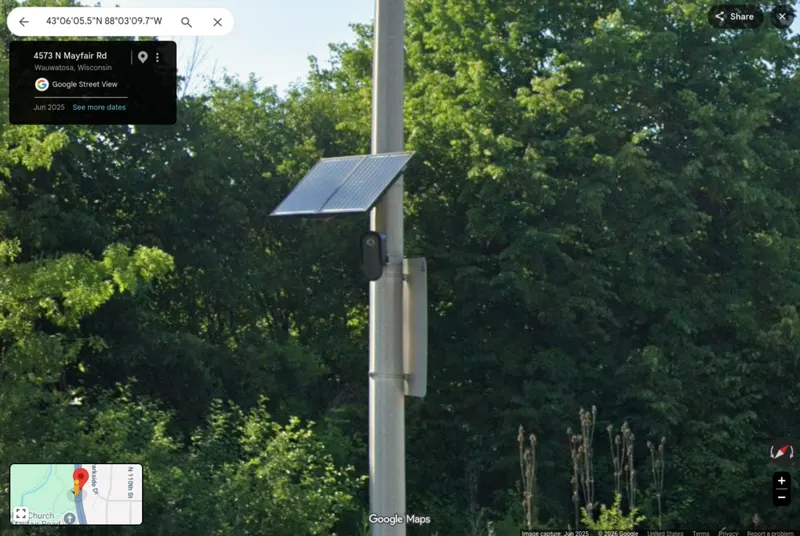
Security researchers have identified serious flaws in Flock cameras used for automatic license plate recognition (ALPR). The devices run on outdated software, making them vulnerable to unauthorized access to the company's production infrastructure.
Analysis showed that the equipment operates on Android 8.1 and Linux 3.18 kernel. These OS versions have not received critical security updates for a long time, leaving the system open to exploitation of known exploits. Additionally, hard-coded API keys were found in the camera firmware, which provide access to cloud services and data transmitted from the devices.
The use of outdated components in surveillance systems, which are widely used by law enforcement agencies, creates a risk of confidential information leakage. The presence of static credentials allows attackers to bypass authentication mechanisms, gaining control over real-time data streams. Details of the technical audit and discussion of the incident's consequences are available on the Lobste.rs platform.
This situation highlights the security problem in the segment of IoT devices with AI functions, where the speed of introducing new algorithms often outpaces the process of updating the underlying software. The lack of regular patches and the use of insecure methods for storing access keys in such systems threaten the privacy of data collected using computer vision technologies.
Related news
 Nvidia accused of supplying chips to shell companies in China
November 7, 2026
 Google has acquired a data center site from Crusoe in Wyoming
November 6, 2026
 Chinese intelligence attempted to recruit a top executive for Nvidia
November 6, 2026
 OpenAI has raised an additional $11 billion
November 6, 2026