 mozgi
Cybersecurity expert hacked the BYD Shark 6 electric vehicle
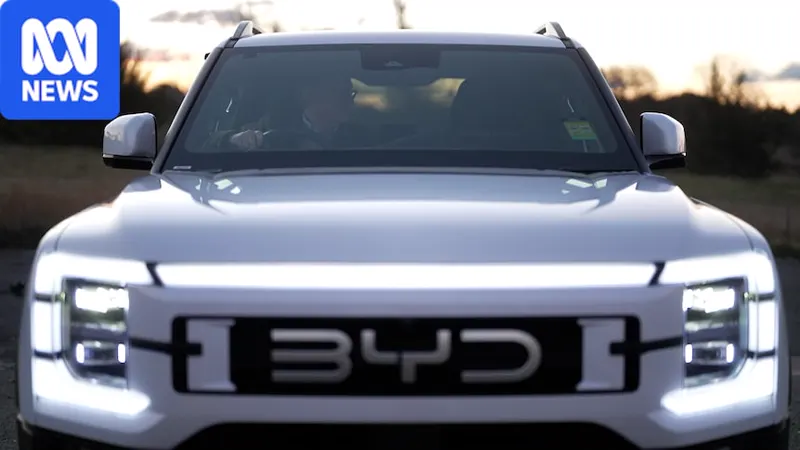
A cybersecurity specialist successfully conducted a remote hack of a BYD Shark 6 pickup, demonstrating critical vulnerabilities in the vehicle's software, and gained full control over key functions of the car without physical access to it.
The main reason for the hack was the lack of basic password protection in the control system, allowing the researcher to remotely activate the lighting fixtures, control the windshield wipers, and access the infotainment system. Such a vulnerability allows attackers not only to track the owner's movements but also to create emergency situations on the road by hijacking control of secondary electronic nodes.
The incident sparked serious discussions in the professional community, including discussions on Hacker News, where experts emphasized the risks associated with the integration of cloud services into modern cars, and the lack of multi-factor authentication and weak data encryption protocols make connected cars vulnerable to sabotage and covert surveillance attacks.
Electric vehicle manufacturers are increasingly facing the need to revise the security architecture of their systems, and this case shows that even modern models with advanced software can be compromised due to elementary errors in access configuration, requiring the implementation of stricter cybersecurity standards in the automotive industry.
Related news
 United has banned third-party AI agents from booking tickets
November 11, 2026
 US business spending on AI has slowed to 1.65 percent
November 11, 2026
 CoreWeave changes its financing model to scale infrastructure
November 11, 2026
 TSMC to invest up to $1 billion in Anthropic and OpenAI
November 11, 2026