 mozgi
Researcher gains full access to Meta Ray-Ban firmware

An independent security researcher has successfully hacked Meta Ray-Ban smart glasses, gaining full control over the device's software. During the experiment, the researcher managed to extract the gadget's complete firmware by exploiting a GraphQL flag vulnerability that allowed bypassing standard access restrictions.
To carry out the attack, the author replaced the legitimate Device Access Toolkit APK file with their own version, signed with their own key. Using the Frida tool allowed for code injection into the runtime environment and the setup of a bind shell for device debugging. This method provided access to internal processes of the glasses that are typically hidden from users and third-party app developers.
The obtained data allows for a deeper study of the architecture of how wearable devices interact with the Meta ecosystem. Such research highlights vulnerabilities in the security of consumer electronics with integrated AI features, emphasizing the importance of verifying authentication mechanisms in firmware that interacts with cloud APIs.
Related news
 OpenAI has opened outbound SIP calling to all organizations
November 6, 2026
 Replit has updated its sandbox engine based on microVMs
November 6, 2026
 Meta has added a spaces feature to customize the Muse AI assistant
November 6, 2026
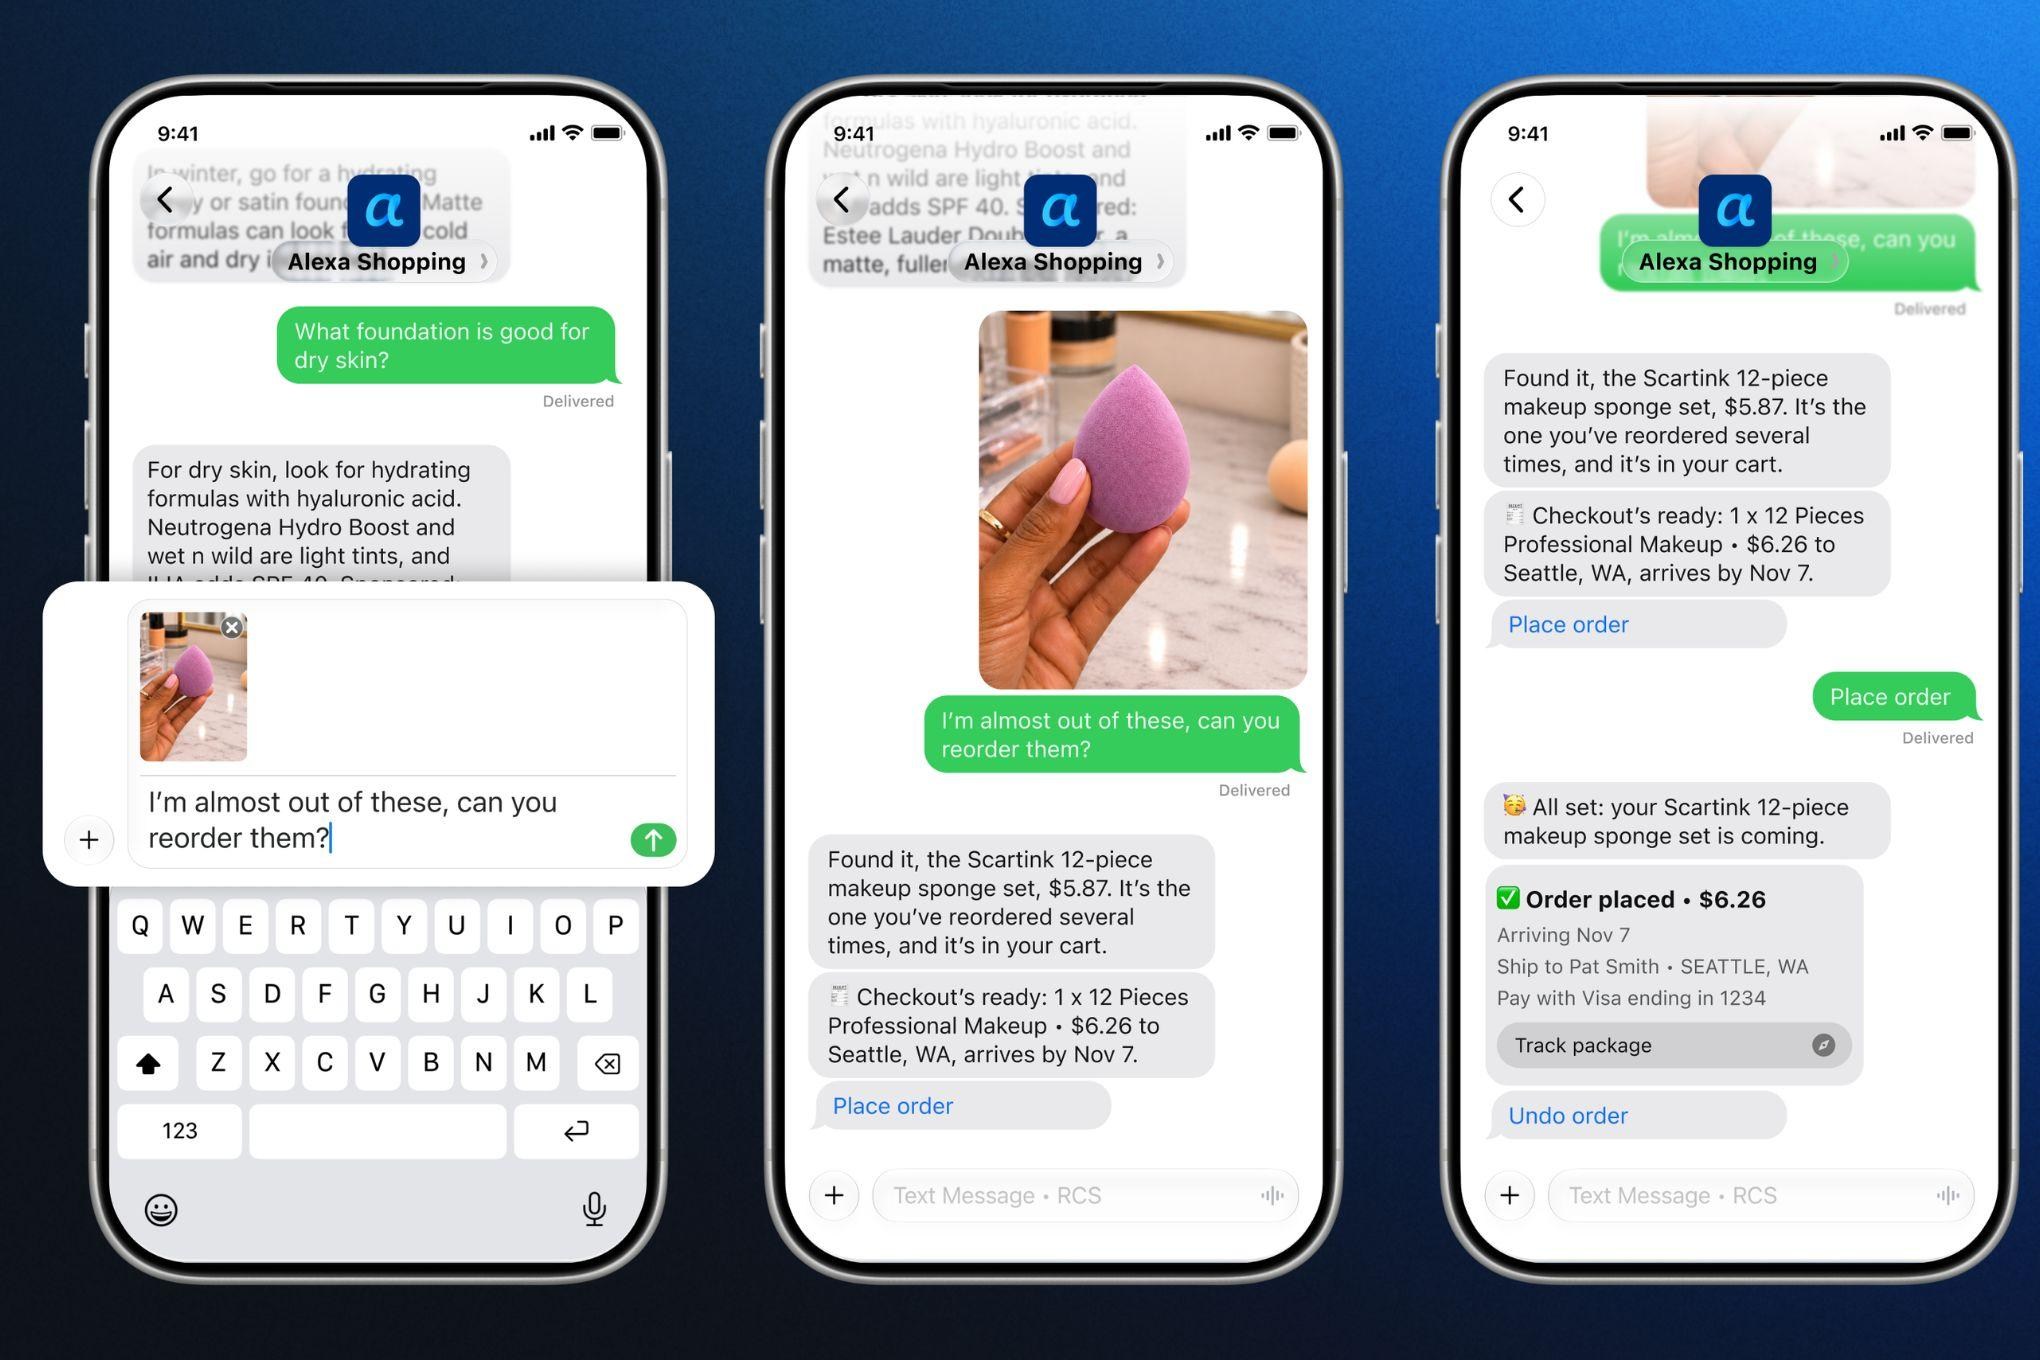 Amazon has added text search and ordering to Alexa for Shopping
November 6, 2026